Showing posts sorted by date for query Linux. Sort by relevance Show all posts

June 6, 2023

Kali Linux 2023.2: A Comprehensive Update for the Popular Security Distribution


Kali Linux, a popular distribution for penetration testing and ethical hacking, has released its latest version, 2023.2. This release includes a number of new features and tools, as well as updates to existing ones.

Here are some of the highlights of Kali Linux 2023.2:

  • New VM image for Hyper-V: Kali Linux now includes a pre-built VM image for Hyper-V, making it easier to use Kali on Windows systems.
  • Xfce audio stack update: The Xfce audio stack has been updated to PipeWire, which should improve audio performance on Kali systems.
  • i3 desktop overhaul: The i3 desktop environment has been overhauled, with a number of new features and improvements.
  • Desktop updates: A number of other desktop updates have been made, including easy hashing in Xfce and a new version of GNOME.
  • New tools: A number of new tools have been added to Kali Linux, including Evilginx, a framework for stealing credentials and session cookies.

Kali Linux 2023.2 is available for download now. To learn more about this release, please visit the Kali Linux website.

Here are some additional details about the new features and tools in Kali Linux 2023.2:

  • New VM image for Hyper-V: The new Hyper-V VM image for Kali Linux makes it easy to use Kali on Windows systems. The image includes all of the necessary tools and software for penetration testing and ethical hacking, and it can be used with both Hyper-V Server and Hyper-V on Windows 10 or Windows 11.
  • Xfce audio stack update: The Xfce audio stack has been updated to PipeWire, which is a new audio server that is designed to replace PulseAudio. PipeWire offers a number of advantages over PulseAudio, including better performance, more features, and better security.
  • i3 desktop overhaul: The i3 desktop environment has been overhauled with a number of new features and improvements. These include a new layout manager, a new window manager, and a new set of icons.
  • Desktop updates: A number of other desktop updates have been made, including easy hashing in Xfce and a new version of GNOME. Easy hashing makes it easy to hash files and strings in Xfce, and the new version of GNOME includes a number of new features and improvements, such as a new dark mode and a new file manager.
  • New tools: Kali Linux 2023.2 includes a number of new tools, including:
    • Evilginx: Evilginx is a new framework for stealing credentials and session cookies. It can be used to create fake login pages that look like legitimate websites. When users enter their credentials on the fake page, Evilginx will capture them and send them back to the attacker.
    • Wifiphisher: Wifiphisher is a new tool for phishing wireless networks. It can be used to create fake access points that look like legitimate networks. When users connect to the fake network, Wifiphisher will redirect them to a malicious website that can be used to steal their credentials.
    • Pentoo: Pentoo is a new penetration testing distribution based on Kali Linux. It includes a number of additional tools and features that are designed for penetration testing.

Kali Linux 2023.2 is a significant release that includes a number of new features and tools. If you are a user of Kali Linux, I encourage you to upgrade to this new release.


For more information on the new features and improvements in Kali Linux 2023.2, please visit the Kali Linux website: https://www.kali.org/


#kali #linux #update #2023

May 23, 2023

How to Safeguard Chrome: Removing the Google Docs Offline Extension Virus


Have you noticed that your Chrome browser is acting strangely or that your computer is slowing down? If you have the "Google Docs" extension installed, you might be a victim of a malicious virus.

The "Google Docs" extension is a fake extension that claims to be an official Google tool for working with Google Docs. However, it is actually a virus that can harm your computer and steal your personal information.

So, what are the reasons for this virus? Most likely, you unknowingly installed it while browsing the internet. Malicious websites often trick users into downloading and installing fake extensions by disguising them as legitimate ones.

The virus can do a variety of things, such as stealing your personal information, displaying unwanted ads, and redirecting you to suspicious websites. It can even take over your browser and display pop-ups and other annoying messages.


So, how can you remove this virus permanently from your Chrome browser? Here are the steps you need to take:


1) Remove the "Google Docs" extension: Go to your Chrome browser's settings and locate the "Extensions" tab. Find the "Google Docs" extension and click on the trash bin icon to remove it.  


2) Clear your browser data: Open your browser's settings and go to "Privacy and security." Click on "Clear browsing data" and select "All time" as the time range. Check all the boxes and click on "Clear data."


3) Run a malware scan: Use a reliable anti-malware software to scan your computer for any other viruses or malware that might be present.


4) Stop syncing data to your Google account: If you have synced your Chrome browser data with your Google account, make sure to stop the syncing. This will ensure that the virus won't reappear again.


5) Uninstall and reinstall Chrome: If the virus is still present even after following the above steps, consider uninstalling and reinstalling Chrome. This will remove any traces of the virus that might be hiding deep within your browser.


6) Change your passwords:
If you have used the affected computer to access any sensitive accounts, such as banking or email, change your passwords immediately.


7) Be cautious when downloading extensions: Make sure to only download extensions from trusted sources, such as the official Chrome Web Store.


By following these steps, you can remove the "Google Docs" extension virus and protect your computer from further harm. Remember to stay vigilant when browsing the internet and always be cautious when downloading any software or extensions.


Also Read -

Flight Tracking Made Easy: A Step-by-Step Guide to Using dump1090-mutability on Linux

How to Secure Your Linux System by Adding a Bootloader Password

DIY WiFi Repeater with an ESP8266: A Step by Step Guide

April 5, 2023

Flight Tracking Made Easy: A Step-by-Step Guide to Using dump1090-mutability on Linux


 Have you ever wondered about the planes flying overhead? What airline they belong to? Where they're going? Well, wonder no more! With the help of ADS-B (Automatic Dependent Surveillance-Broadcast), you can track flights in your area using a simple software package called dump1090-mutability. And the best part? You can do it all from the comfort of your own Linux machine. In this step-by-step installation guide, we'll show you how to get started.


Step 1: Installing dump1090-mutability


The first step is to install dump1090-mutability on your Linux machine. We'll assume that you're running Ubuntu or Debian, but the installation process should be similar for other Linux distributions. Open a terminal window and enter the following command:


$ sudo apt-get update
$ sudo apt-get install dump1090-mutability rtl-sdr

Step 2: Running dump1090-mutability


Now that you've installed and configured dump1090-mutability, it's time to run it. Open a terminal window and enter the following command:


$ sudo dump1090-mutability --interactive


This will start dump1090-mutability and display the ADS-B data from nearby aircraft in real-time.


Step 3: Viewing Metric Units


By default, dump1090-mutability displays the output in imperial units. If you prefer metric units, you can use the following command instead:


$ sudo dump1090-mutability --metric  --interactive 


This will display the ADS-B data in metric units.


Conclusion -


Tracking flights with ADS-B using dump1090-mutability is a fun and educational project that can be easily accomplished with a Linux machine. By following this step-by-step installation guide, you'll be able to view the ADS-B data from nearby aircraft and learn more about the planes flying overhead. So why not give it a try? Who knows what kind of interesting flights you'll discover!


Also Read - 


How to create a ESP8266 Wi-Fi Deauthenticator in just $4


DIY WiFi Repeater with an ESP8266: A step by step Guide 


How to Secure Your Linux System by Adding a Bootloader Password

January 8, 2023

How to Secure Your Linux System by Adding a Bootloader Password


The GRUB (Grand Unified Bootloader) is a bootloader that is used by many Linux distributions to boot the operating system. You can set a password for GRUB to protect the boot process and prevent unauthorized changes to the boot options.

To set a password for GRUB in Linux, follow these steps:
 

1) Open a terminal window on your Linux machine.

2) Run the grub-mkpasswd-pbkdf2 command to generate a password hash. For example:

$ sudo grub-mkpasswd-pbkdf2


This will prompt you to enter a password and confirm it. The command will then output a password hash.


3) Edit the GRUB configuration file using a text editor. The file is usually located at /etc/grub.d/40_custom, but the location may vary depending on your distribution.


$ sudo nano /etc/grub.d/40_custom


4) Add the following lines to the configuration file, replacing <username> with your desired username and <password_hash> with the password hash generated in step 2:

set superusers="{username}"
password_pbkdf2 {username} {password_hash}


5) Save and close the configuration file. 


6) Run the update-grub command to update the GRUB configuration.


$ sudo update-grub


7) Reboot your machine and test the password by pressing e at the GRUB boot menu to edit the boot options. You should be prompted for the password before you can make any changes.

It's important to note that the password protection provided by GRUB is only as secure as the password you set. Choose a strong, unique password to protect your system from unauthorized access.

That's it! If you have any problem regarding this, please comment below. 


Also Read -

How to create a ESP8266 Wi-Fi Deauthenticator in just $4

DIY WiFi Repeater with an ESP8266: A Step by Step Guide 

How to do rogue AP attack in Linux using WifiPumpkin3

January 4, 2023

DIY WiFi Repeater with an ESP8266: A Step by Step Guide


The ESP8266 is a low-cost, low-power microcontroller with built-in WiFi support. It was originally developed by Espressif Systems as a solution for offloading WiFi networking functions from more expensive, power-hungry microprocessors.

An ESP8266 WiFi repeater, also known as a WiFi range extender, takes an existing WiFi signal and rebroadcasts it to create a second network. This can be used to extend the range of a WiFi network, or to provide wireless connectivity to devices that are out of range of the main network.


To set up an ESP8266 WiFi repeater, you will need:


  • An ESP8266 development board, such as the NodeMCU or Wemos D1 mini or Lolin
  • A USB data cable, to power the ESP8266
  • The Arduino IDE software, which you can download for free from the Arduino website (https://www.arduino.cc/en/Main/Software)


1] First you need to configure the ESP8266 in the Arduino IDE, follow these steps:

  1. Download and install the Arduino IDE from the Arduino website (https://www.arduino.cc/en/Main/Software).
  2. Connect your ESP8266 development board to your computer using a USB cable.
  3. Open the Arduino IDE and go to "File" > "Preferences".
  4. In the "Additional Board Manager URLs" field, enter the following URL: http://arduino.esp8266.com/stable/package_esp8266com_index.json
  5. Click "OK" to close the Preferences window.
  6. Go to "Tools" > "Board: " > "Boards Manager...".
  7. In the Boards Manager, search for "esp8266" and click on the "Install" button for the "esp8266" entry.
  8. Wait for the installation to complete, then close the Boards Manager window.
  9. Go to "Tools" > "Board: " and select your ESP8266 board from the list. The exact board name will depend on the specific ESP8266 development board you are using.
  10. Go to "Tools" > "Port" and select the COM port for your ESP8266. The COM port should appear as "USB-SERIAL CH340 (COMxx)" or "FT232R USB UART (COMxx)".


2] After configuration, Copy and paste the following code into the Arduino IDE, replacing "your_ssid" and "your_password" with the SSID and password of your existing WiFi network:


#include 
 //Replace Your Router's SSID and password.

const char * ssid = "your_ssid";
const char * password = "your_password";

// Replace ESP Wifi SSID and Password

const char * ssid_soft_ap = "ESPRepeater";
const char * pwd_soft_ap = "Pass@12345"
int Wifi_SoftAP_Channel = 9;

// Rename ESP name to find easily on your router

const char * espHostname = "ESPRepeater";
void setup() {
  WiFi.mode(WIFI_AP_STA);
  WiFi.begin(ssid, password);
  while (WiFi.status() != WL_CONNECTED) {
    WiFi.hostname(espHostname);
    delay(500);
  }
  WiFi.softAP(ssid_soft_ap, pwd_soft_ap, Wifi_SoftAP_Channel);
}
void loop() {}


3] Click the "Upload" button to upload the code to the ESP8266.


4] Once the code has been uploaded, open the serial monitor in the Arduino IDE. The ESP8266 should connect to your existing WiFi network and display its IP address.


5] Connect a device to the ESP8266's WiFi network and verify that it is able to connect to the internet.


That's it! Your ESP8266 should now be functioning as a WiFi repeater, rebroadcasting the signal from your existing WiFi network and providing wireless connectivity to devices that are out of range.

Also Read -

How to create a ESP8266 Wi-Fi Deauthenticator in just $4

How to do rogue AP attack in Linux using WifiPumpkin3 

Enable monitor mode in linux without disconnecting Wi-Fi

December 11, 2022

How to create a ESP8266 Wi-Fi Deauthenticator in just $4


The ESP8266 is designed to work with microcontroller boards like Arduino and Raspberry Pi, making it easy to integrate into existing projects with minimal overhead. The ESP8266 is a low-cost microcontroller that can be programmed to operate as a stand-alone system or as an embedded part of a larger product. It has built-in Wi-Fi connectivity, which allows it to connect to other devices and send/receive data from them.

This project is to build a simple ESP8266 Universal Wifi Deauthenticator. The esp8266 can simply deauthenticate other networks that are connected to your router and disconnect them, causing the connected network to reconnect slowly over time. This method can be used to delay an attacker's time in the network so they cannot compromise it. ESP8266 will send a packet requesting that it connected to the protected network. As soon as this happens, all clients will shut down immediately so they won't create any traffic on WiFi network.

In this post, we're going to create esp8266 wifi jammer or deauthenticator in simple steps.


Requirements - 

1) An ESP8266 module

2) USB data cable


Installation -

1) First we need to install drivers according to chipset. There are 2 types of chipset - CH34x and CP210x. So identify chipset and install drivers according to your module.

Download Drivers for CH340

Download Drivers for CP210x 


2) After this, download flasher tool from Github link. 

Download N2D2 Flasher Tool 


3) Now Extract zip file and launch N2D2 tool


4) Now connect ESP8266 using USB Data Cable to Laptop / Desktop

5) The tool will automatically detects drivers and you device


6) Select 'Get the latest image from internet'


7) Now select software version for your device. We need software which ends with 'DSTIKE_DEAUTHER_V1'. You can choose V2 or V3. After this, it will download latest software from Github.


8) Now Select 'Allow software installation'


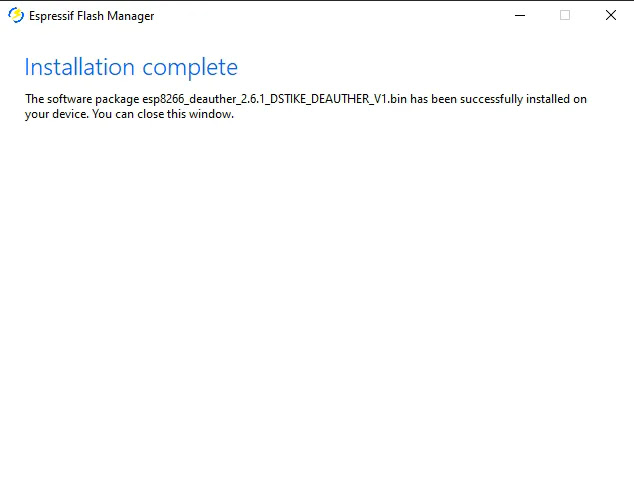
9)  After successful installation, close the tool.


How to use -

1) Connect your device to esp8266 using wifi. You can see the network name 'pwned'. Use password "deauther" to connect to the esp8266.


2) When device connects, Open you browser and go to this address -

192.168.4.1


3) Click on "I have read and understood the notice above"


4) Now you will get all wi-fi networks available near to you. Select any one or multiple networks from list


5) Now goto the topmost navbar and select 'Attack' option. You will be redirected to attack page. You will get 3 options. Select any option of your choice


How these 3 options works -

1] Deauth

Closes the connection of WiFi devices by sending deauthentication frames to access points and client devices you selected.
This is only possible because a lot of devices don't use the 802.11w-2009 standard that offers a protection against this attack.
Please only select one target! When you select multiple targets that run on different channels and start the attack, it will quickly switch between those channels and you have no chance to reconnect to the access point that hosts this web interface.
 

2] Beacon

Beacon packets are used to advertise access points. By continuously sending beacon packets out, it will look like you created new WiFi networks.
You can specify the network names under SSIDs.
 

3] Probe

Probe requests are sent by client devices to ask if a known network is nearby.
Use this attack to confuse WiFi trackers by asking for networks that you specified in the SSID list.
It's unlikely you will see any impact by this attack with your home network.


That's it. Don't use this for illegal purposes.


TAGS -

#wifi-jammer #wifi-deauthenticator #esp8266 #nodemcu


Also Read -

Useful OSINT tool for bug hunters - Photon

Enable monitor mode in linux without disconnecting wifi 


November 20, 2022

Useful OSINT tool for bug hunters - Photon [2024]


OSINT tool is an open source intelligence (OSINT) tool designed to search for subdomains, web archives, and other related information. It works by using Google's API to pull data from the site, then processes it through a number of different filters before presenting it back to the user in a clean and easy-to-read interface.


In this post, we are going to discuss about a OSINT tool - Photon. Photon is a python-based tool which is useful in various purposes like Website cloning, find archive pages and subdomains of any website. 


Photon can extract the following data while crawling:

  • URLs (in-scope & out-of-scope)
  • URLs with parameters
  • Intel (emails, social media accounts, amazon buckets etc.)
  • Files (pdf, png, xml etc.)
  • Secret keys (auth/API keys & hashes)
  • JavaScript files & Endpoints present in them
  • Strings matching custom regex pattern
  • Subdomains & DNS related data


Installation

1) Update packages

$ sudo apt update


2) Install required packages

$ sudo apt install python git


3) Clone Photon from Github

$ git clone https://github.com/s0md3v/Photon


4) Install requirements

$ cd Photon
$ sudo pip3 install -r requirements.txt


5) Now run this tool

$  python3 photon.py -h


You will see instructions to use Photon


How to Use -


1) To find all URLs in any website

You can easily find all URLs including hidden URL by using this -

$ python3 photon.py -u http://testphp.vulnweb.com/ --only-urls


2) To clone website

You can easily clone any website by using this -

$ python3 photon.py -u http://testphp.vulnweb.com/ --clone


3) To find subdomains

You can easily find subdomains and DNS data of any website by using this -

$ python3 photon.py -u http://testphp.vulnweb.com/ --dns


Output will be stored in the directory format of website's name.


If you're facing any issues regarding this, please comment below.


Related Information - 


Also Read - 

Fix Termux repository related issues [2022]

How to create metasploit payload easily using Linux and Termux


Tags -

#linux #OSINT #tool #termux #subdomain-finder

April 16, 2022

Fix screen resolution of Ubuntu in VMware workstation [2022]


 If you install Ubuntu on VMware workstation, there are some issues which you need to fix. The most common issue we face about Ubuntu is screen resolution. After installing Ubuntu, we got a small screen resolution of Ubuntu. There are other ways to fix this issue like using xrandr command, but this is a temporary solution. If you try to fix this using other ways, system will have some errors and maybe the entire GUI will fail. So in this post we are going to fix this issue. 


Solution - 


1) First update all packages 


$ sudo apt-get update


2) Now install Open VM Tools 


$ sudo apt-get install open-vm-tools-desktop


After this command, screen will automatically fix to correct resolution. If not, try to reboot your system and then check it. 

That's it ! 

If you have any issue regarding this, Leave a comment ! 


Also read -

Enable monitor mode without disconnecting wifi in Linux

How to do rouge AP attack using Wifipumpkin3

December 7, 2021

Enable monitor mode in linux without disconnecting Wi-Fi

 To hack a Wi-Fi network using Linux, you need a wireless card which support monitor mode and packet injction. To carry out these attacks, we need to connect an external wifi adapter that supports monitor mode, but if we want to use the Internet, the adapter disconnects from the wifi network and enters monitor mode. So, if we want internet connectivity, we need to connect another Wi-Fi adapter. So, to overcome this problem, there is a solution that helps you to use Wi-Fi connectivity and packet injection at the same time using only one adapter. So follow these steps to use the same adapter for both purposes at the same time.


  • Steps -

1) Open terminal and open nano editor


 nano

2) Now paste this code in editor


#!/bin/bash
echo "## Enabling monitor mode on mon0 ##"
echo
sudo iw phy phy0 interface add mon0 type monitor && sudo ifconfig mon0 up
echo "## mon0 should be up:"
sudo ip link show dev mon0

3) Now press 'Ctrl + X' and 'Y' and give filename as 'mon0up'


4) Again, open nano editor and paste this code


#!/bin/bash
echo "## Shutting down monitor mode on mon0 ##"
echo
sudo ifconfig mon0 down && sudo iw dev mon0 del
echo "## mon0 should no longer exist:" 
sudo ip link show dev mon0

5) Now press 'Ctrl + X' and 'Y' and give filename as 'mon0down'


6) We have two files mon0up and mon0down. Now we need to give execution permission to these files. So run these commands one by one -


$ sudo chmod +x mon0up
$ sudo chmod +x mon0down

7) Now copy these files to /usr/local/bin


$ sudo cp mon0up /usr/local/bin/
$ sudo cp mon0down /usr/local/bin/

8) Now you can enable monitor mode by typing 'mon0up' and disable it by typing 'mon0down' without disconnecting internet connectivity. To check mon0 interface, run 'iwconfig' command. You will get this output -

9) Now to crack wifi network, you need to use 'mon0' interface instead of 'wlan0mon' or any other else. Just like this -

$ sudo airodump-ng mon0


That's it ! If you have any issue regarding this, please leasve a comment.


Also read -

How to do phishing attack in termux using socialfish

How to do rouge AP attack using wifipumpkin3 


November 12, 2021

How to do rogue AP attack in Linux using WifiPumpkin3


WifiPumpkin3


A rogue access point (or AP) is a wireless access point that is not managed by your network administrator because it is installed on your network without your permission. Rogue APs do not have the same security settings as other access points. These APs are physically located behind a network firewall. This means that anyone who has access to the AP has access to a wider network.  A rogue AP is a wireless access point installed on a wired network infrastructure without the permission of the network administrator or owner to provide rogue wireless access to the network's wired infrastructure. There is likely to be. Anyway, rogue access points can be used in a variety of attacks, including denial of service, data theft, and other malware implementations.
In this post we are going to use WifiPumpkin tool. Wifipumpkin3 is a powerful framework for rogue access point attacks which is written in Python that allows security researchers, red teams, and reverse engineers to set up wireless networks to carry out man-in-the-middle attacks.


Features -
 

  • Creates rogue access point attack
  • Good for Man-in-the-middle attacks   
  • Plenty module for deauthentication attacks
  • Provides Rogue Dns Server
  • Can intercept, inspect, modify and replay web traffic        
  • Provides DNS monitoring service
  • Can harvest credentials
 
 
Installation


1) Update packages


$ sudo apt-get update 


2) Install required packages


$ sudo apt-get install hostapd python3.9-dev libssl-dev libffi-dev build-essential python3.9 python3-pyqt5


3) Install wifipumpkin3


$ git clone https://github.com/P0cL4bs/wifipumpkin3.git
$ cd wifipumpkin3
$ sudo python3 setup.py install


4) Now just run this tool by typing -

$ sudo wifipumpkin3


If you have any problems regrading this, please comment below.


Also Read -

Top 5 Subdomain Takeover Tools for Linux [2021]

How to install kali linux repo in any debian based distro 


November 8, 2021

Top 5 Subdomain Takeover Tools of Github for Linux [2024]


Domain Takeover Tools from Github

Obtaining a subdomain is an attack in which an attacker has complete control over the subdomain. This happens when the provider deletes the web content on the domain but forgets to delete the DNS record.
This error could allow an attacker to gain control of a subdomain, which could allow an attacker to perform any type of attack using that subdomain, including phishing and mapping.
To find out which subdomain is easier to control, you need some tools to find that particular subdomain. That way, you can prevent such attacks. Here are some tools to help you identify subdomains that are easy to adopt.
This will help you find that subdomain. These tools are free to use and display results in less than a minute.

Here are some tools to takover subdomains -


1) subzy

Subzy is a golang tool which helps you to find which subdomain is ready to takeover.
 

Link - https://github.com/LukaSikic/subzy


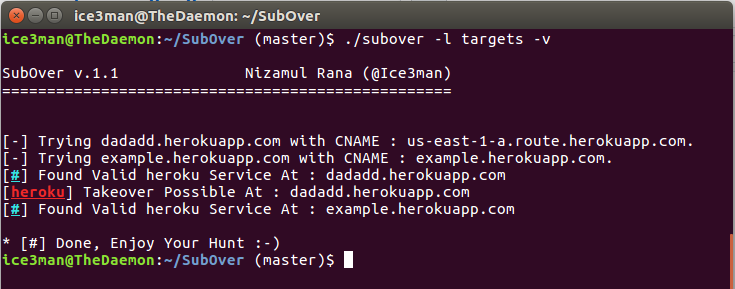
2) SubOver

SubOver is likewise a Go language based tool. It can undoubtedly identify and report vulnerable subdomain that can easily takeover.

Link - https://github.com/Ice3man543/SubOver


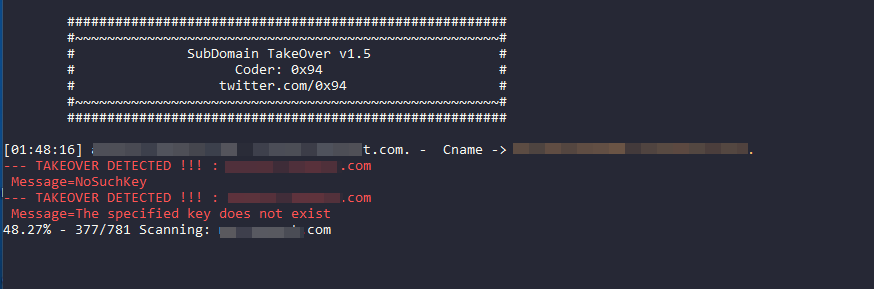
3) takeover


takeover is a Python based tool which recognize a subdomain which is not difficult to takeover.


Link - https://github.com/m4ll0k/takeover


4) subdomain-takeover


This tool also a python based which helps you to find which subdomain is ready to takeover.


Link - https://github.com/antichown/subdomain-takeover


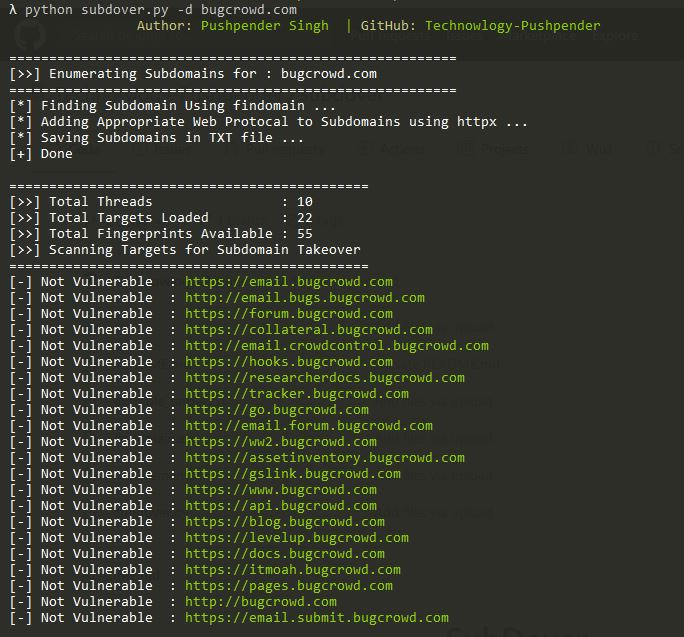
5) subdover

Subdover is a MultiThreaded Subdomain Takeover Vulnerability Scanner Written In Python3, Which has more than 70+ Fingerprints of potentially vulnerable services. Uses CNAME record for verification of findings.


Link - https://github.com/PushpenderIndia/subdover


If you have any query, please comment below.


Also read -

How to do phishing attacks in termux using SocialFish

How to create metasploit payload easily in linux & termux

How to install gui in termux

Termux Posts